Industries / Healthcare
Harmonic Security helps healthcare teams securely adopt AI
Speed up clinical documentation and research safely
Built with leading health systems, payers and life sciences companies, who helped build the models that power Harmonic. See the patient data in every prompt and keep it out of unapproved AI tools.
Talk to us about securing AIWho we work with
Why Harmonic for healthcare
Models that understand medical context
We work with leading health systems, hospitals, payers and life sciences companies, and they have helped build the models that power Harmonic's capabilities. That is why Harmonic recognizes clinical trials data, electronic health records and PHI the way your own teams do. Generic security tools miss that medical context, so they cannot tell safe research from a data breach. Harmonic assesses the entire submission in milliseconds, and unapproved tools stay out of clinical work.
01PHI
Protect patient data and PHI in every prompt
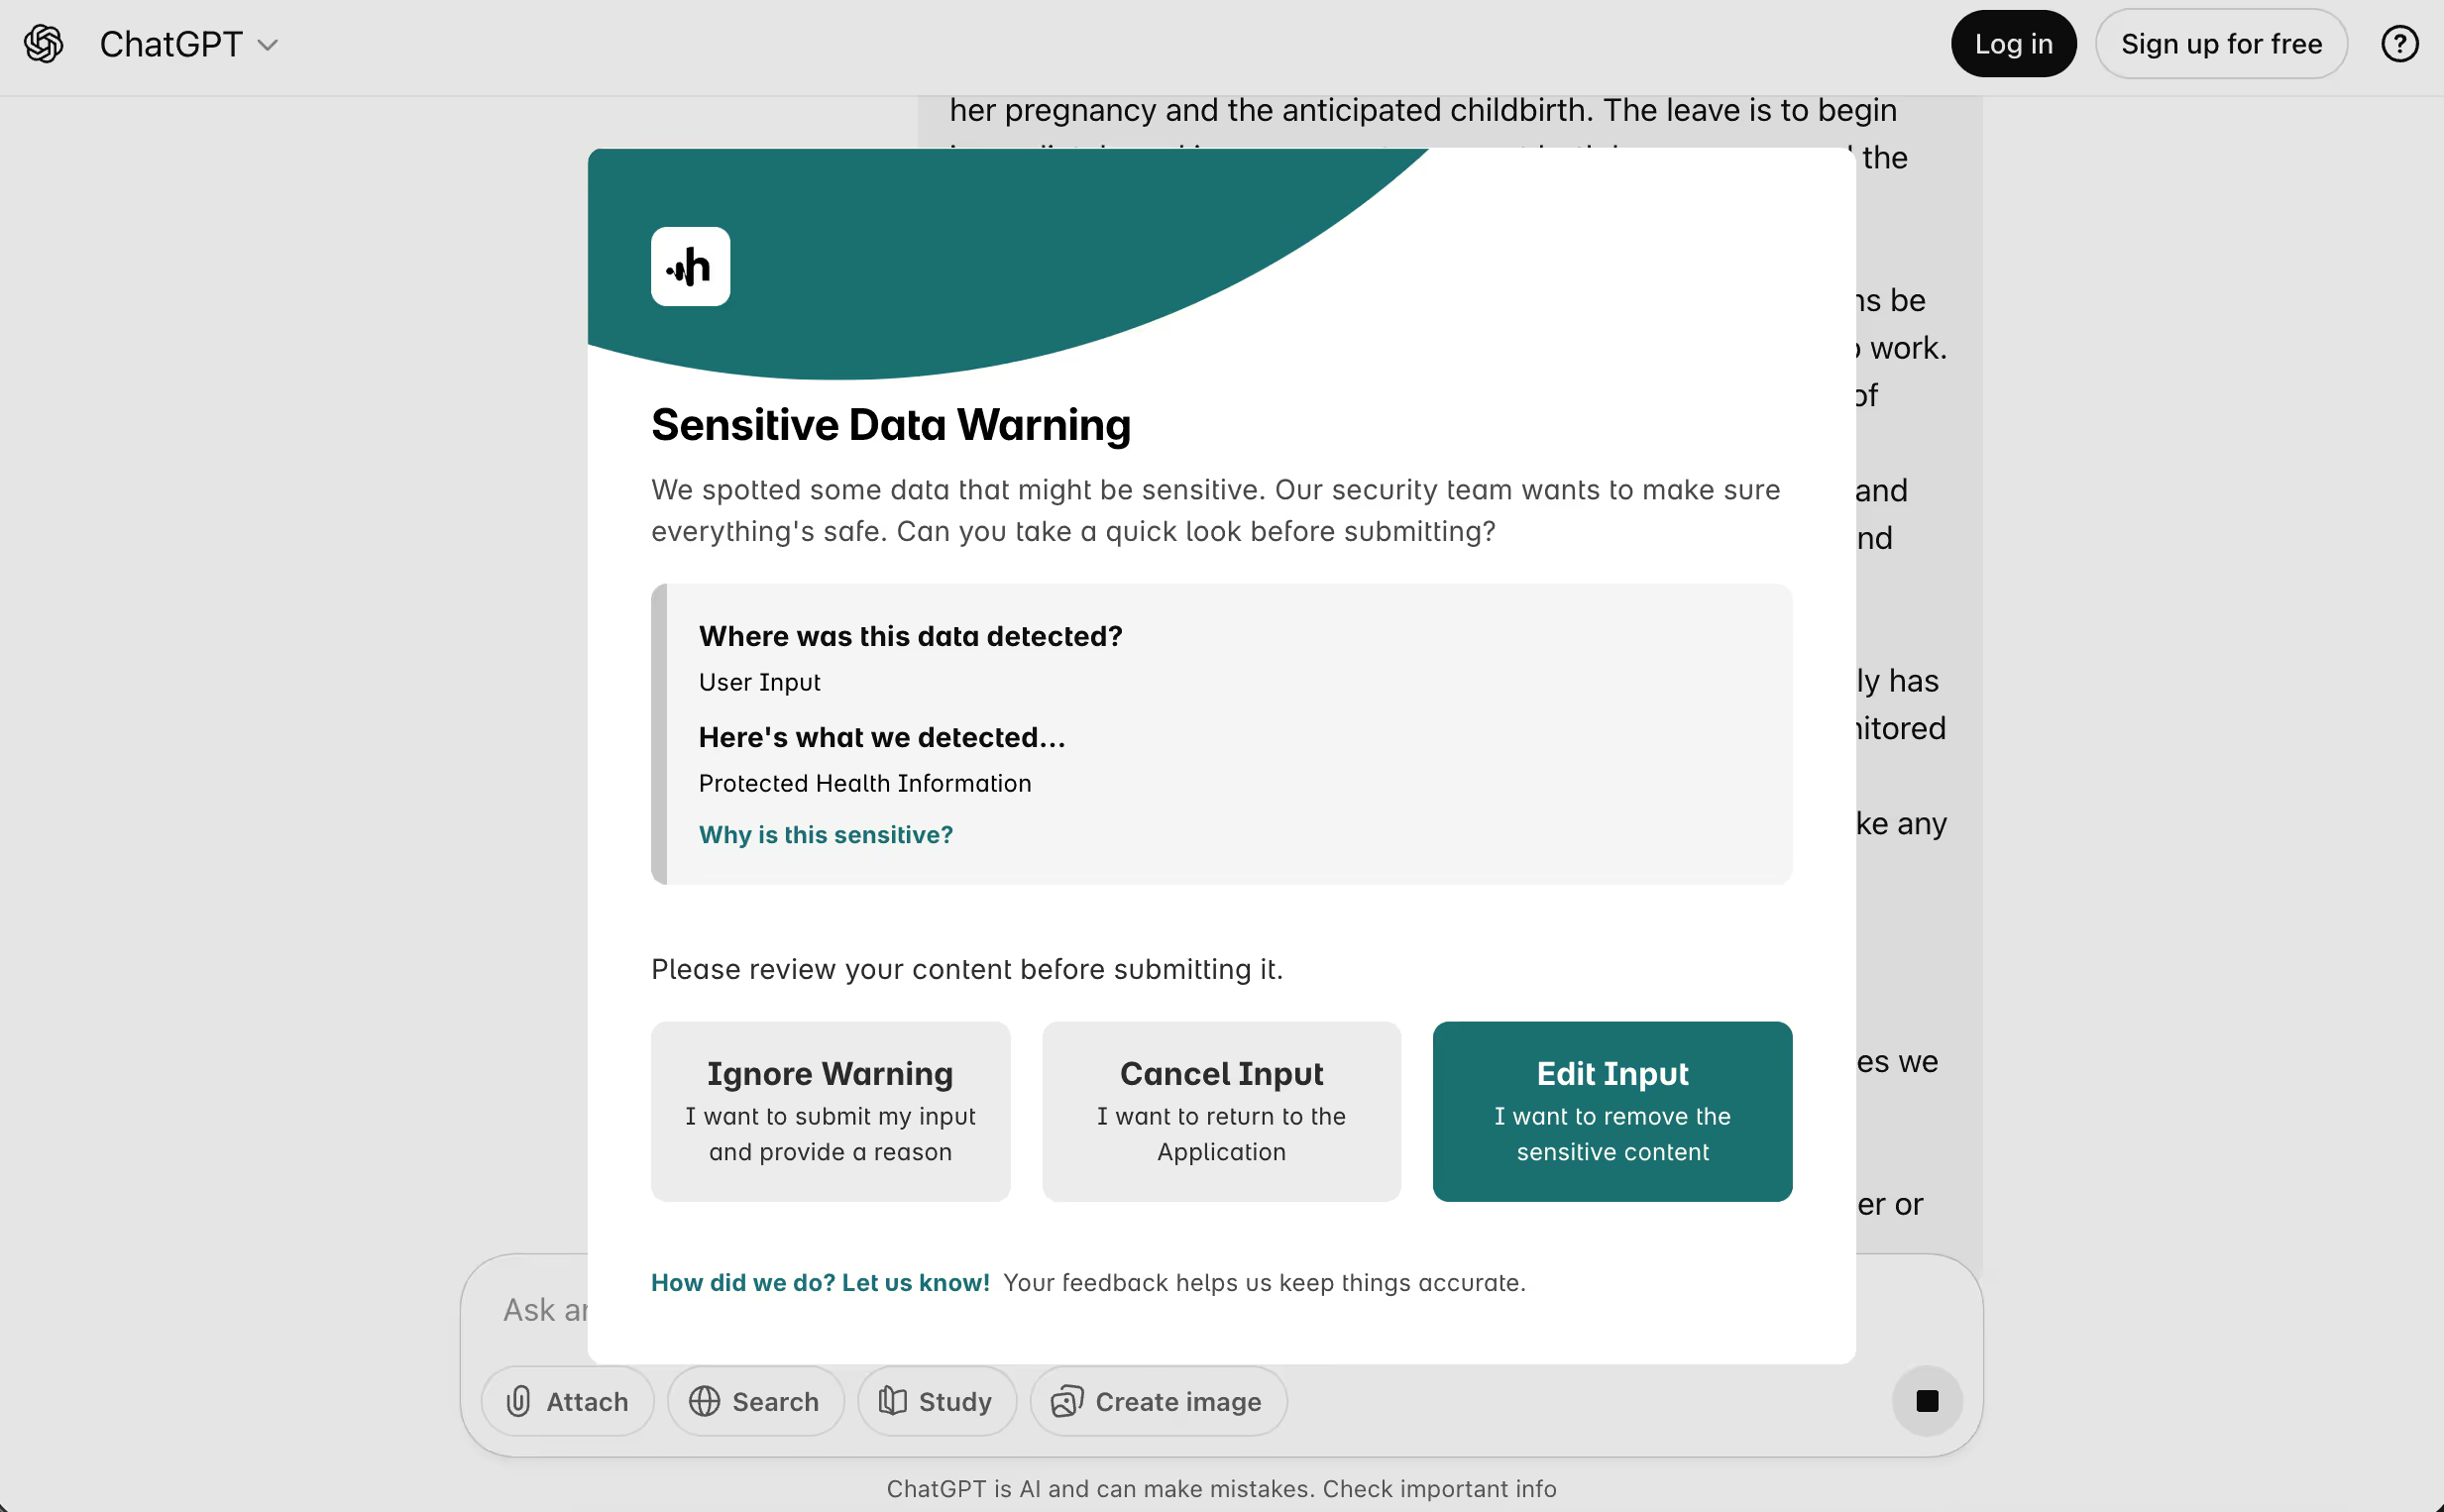
Harmonic assesses the entire submission to AI, not a list of regex patterns. Our PHI model reads each prompt and file in full context, so privacy standards hold even in conversational AI, where a name and a date of birth arrive in the middle of a sentence rather than in a labeled field.
It also recognizes unstructured excerpts from EHR systems, and when EHR data or other PHI heads toward an unapproved AI tool or a personal account, Harmonic blocks it and points the clinician to the approved alternative.
02Research
Protect clinical trials data
Specific models recognize proprietary drug development data, cohorts and study results, and keep them out of public AI models.
That lets research teams use AI on the parts of the work that benefit from it, while the material that carries commercial and regulatory weight stays inside your environment.

03Governance
Put AI governance into practice from day one
Get an immediate inventory of every AI tool in use, with shadow AI surfaced and tools that train on your data flagged, so you can generate reports for stakeholders without a manual audit.
Restrict personal and free accounts for clinical work, and configure policies that block PHI from reaching unapproved tools while permitting safe, de-identified research. If a clinician tries to paste patient notes into an unapproved chatbot, Harmonic intervenes in real time and guides them to a sanctioned instance.
Top resources
Resources for healthcare security teams
How healthcare organizations are governing AI without slowing clinical work.
Frequently asked questions
Quick answers for healthcare teams
Short, direct answers to what clinical security and IT teams ask before bringing Harmonic in.
Why can't security teams just block all AI tools?
AI is embedded in approved productivity tools like Google Translate, Microsoft Copilot and Salesforce, so blocking AI would block core business functions. Employees will also use personal devices and accounts when corporate access is restricted, creating greater shadow AI risk.
Can traditional DLP detect sensitive data in AI prompts?
Traditional regex-based DLP struggles with conversational AI, because prompts are unstructured, contextual, and often contain legitimate business information that patterns cannot distinguish from sensitive data. That leads to false positives and monitor-only deployments.
Do Netskope and Zscaler offer AI-specific controls?
Some SASE vendors offer limited AI controls for a small number of high-profile domains like ChatGPT or Copilot. Those controls require per-domain integrations and do not cover the full spectrum of AI tools, embedded AI features, or agentic workflows.
What is Harmonic Security's technical differentiator?
Harmonic uses purpose-built small language models that understand user intent and sensitive data in milliseconds. This low-latency analysis lets you understand AI usage and enforce inline controls without slowing work down.
Get started
Build your AI guardrails for patient data
Gain the visibility and control you need to guide AI use with confidence. Most teams see first insight in about 30 minutes.
What you'll see with Harmonic Security
- Your full AI usage footprint: every surface, every team, every exposure.
- Inline guardrails that coach, warn, or block, firing in under 200ms.
- See and control what AI agents are actually doing.
- Coverage of browser, endpoint and MCP.
- Deployment in minutes via Intune, JAMF, or Kandji.
