Solutions / Compliance
GenAI compliance for regulated industries
Privacy laws require data protection, and AI safety laws require visibility into how AI is used. Harmonic gives you the controls and evidence to meet both without stalling AI adoption.
Talk to us about securing AIWho we work with
Why Harmonic for compliance
Give auditors the evidence they need without blocking AI outright
Regulators and auditors want evidence that AI use is under control. Harmonic records how employees use AI and applies granular controls to sensitive data and high-risk use cases, so you can answer their questions while your workforce keeps using AI safely.
01Intent
Intent-based control for high-risk use cases
Compliance depends on knowing what people are using AI for, as well as what data they share. Our small language models assess each interaction in full context, in real time.
They identify when AI is being used for high-risk activities such as automated candidate screening or credit scoring, so you can apply the specific guardrails the EU AI Act and local laws require.

02Privacy
Protect data privacy under HIPAA and GDPR
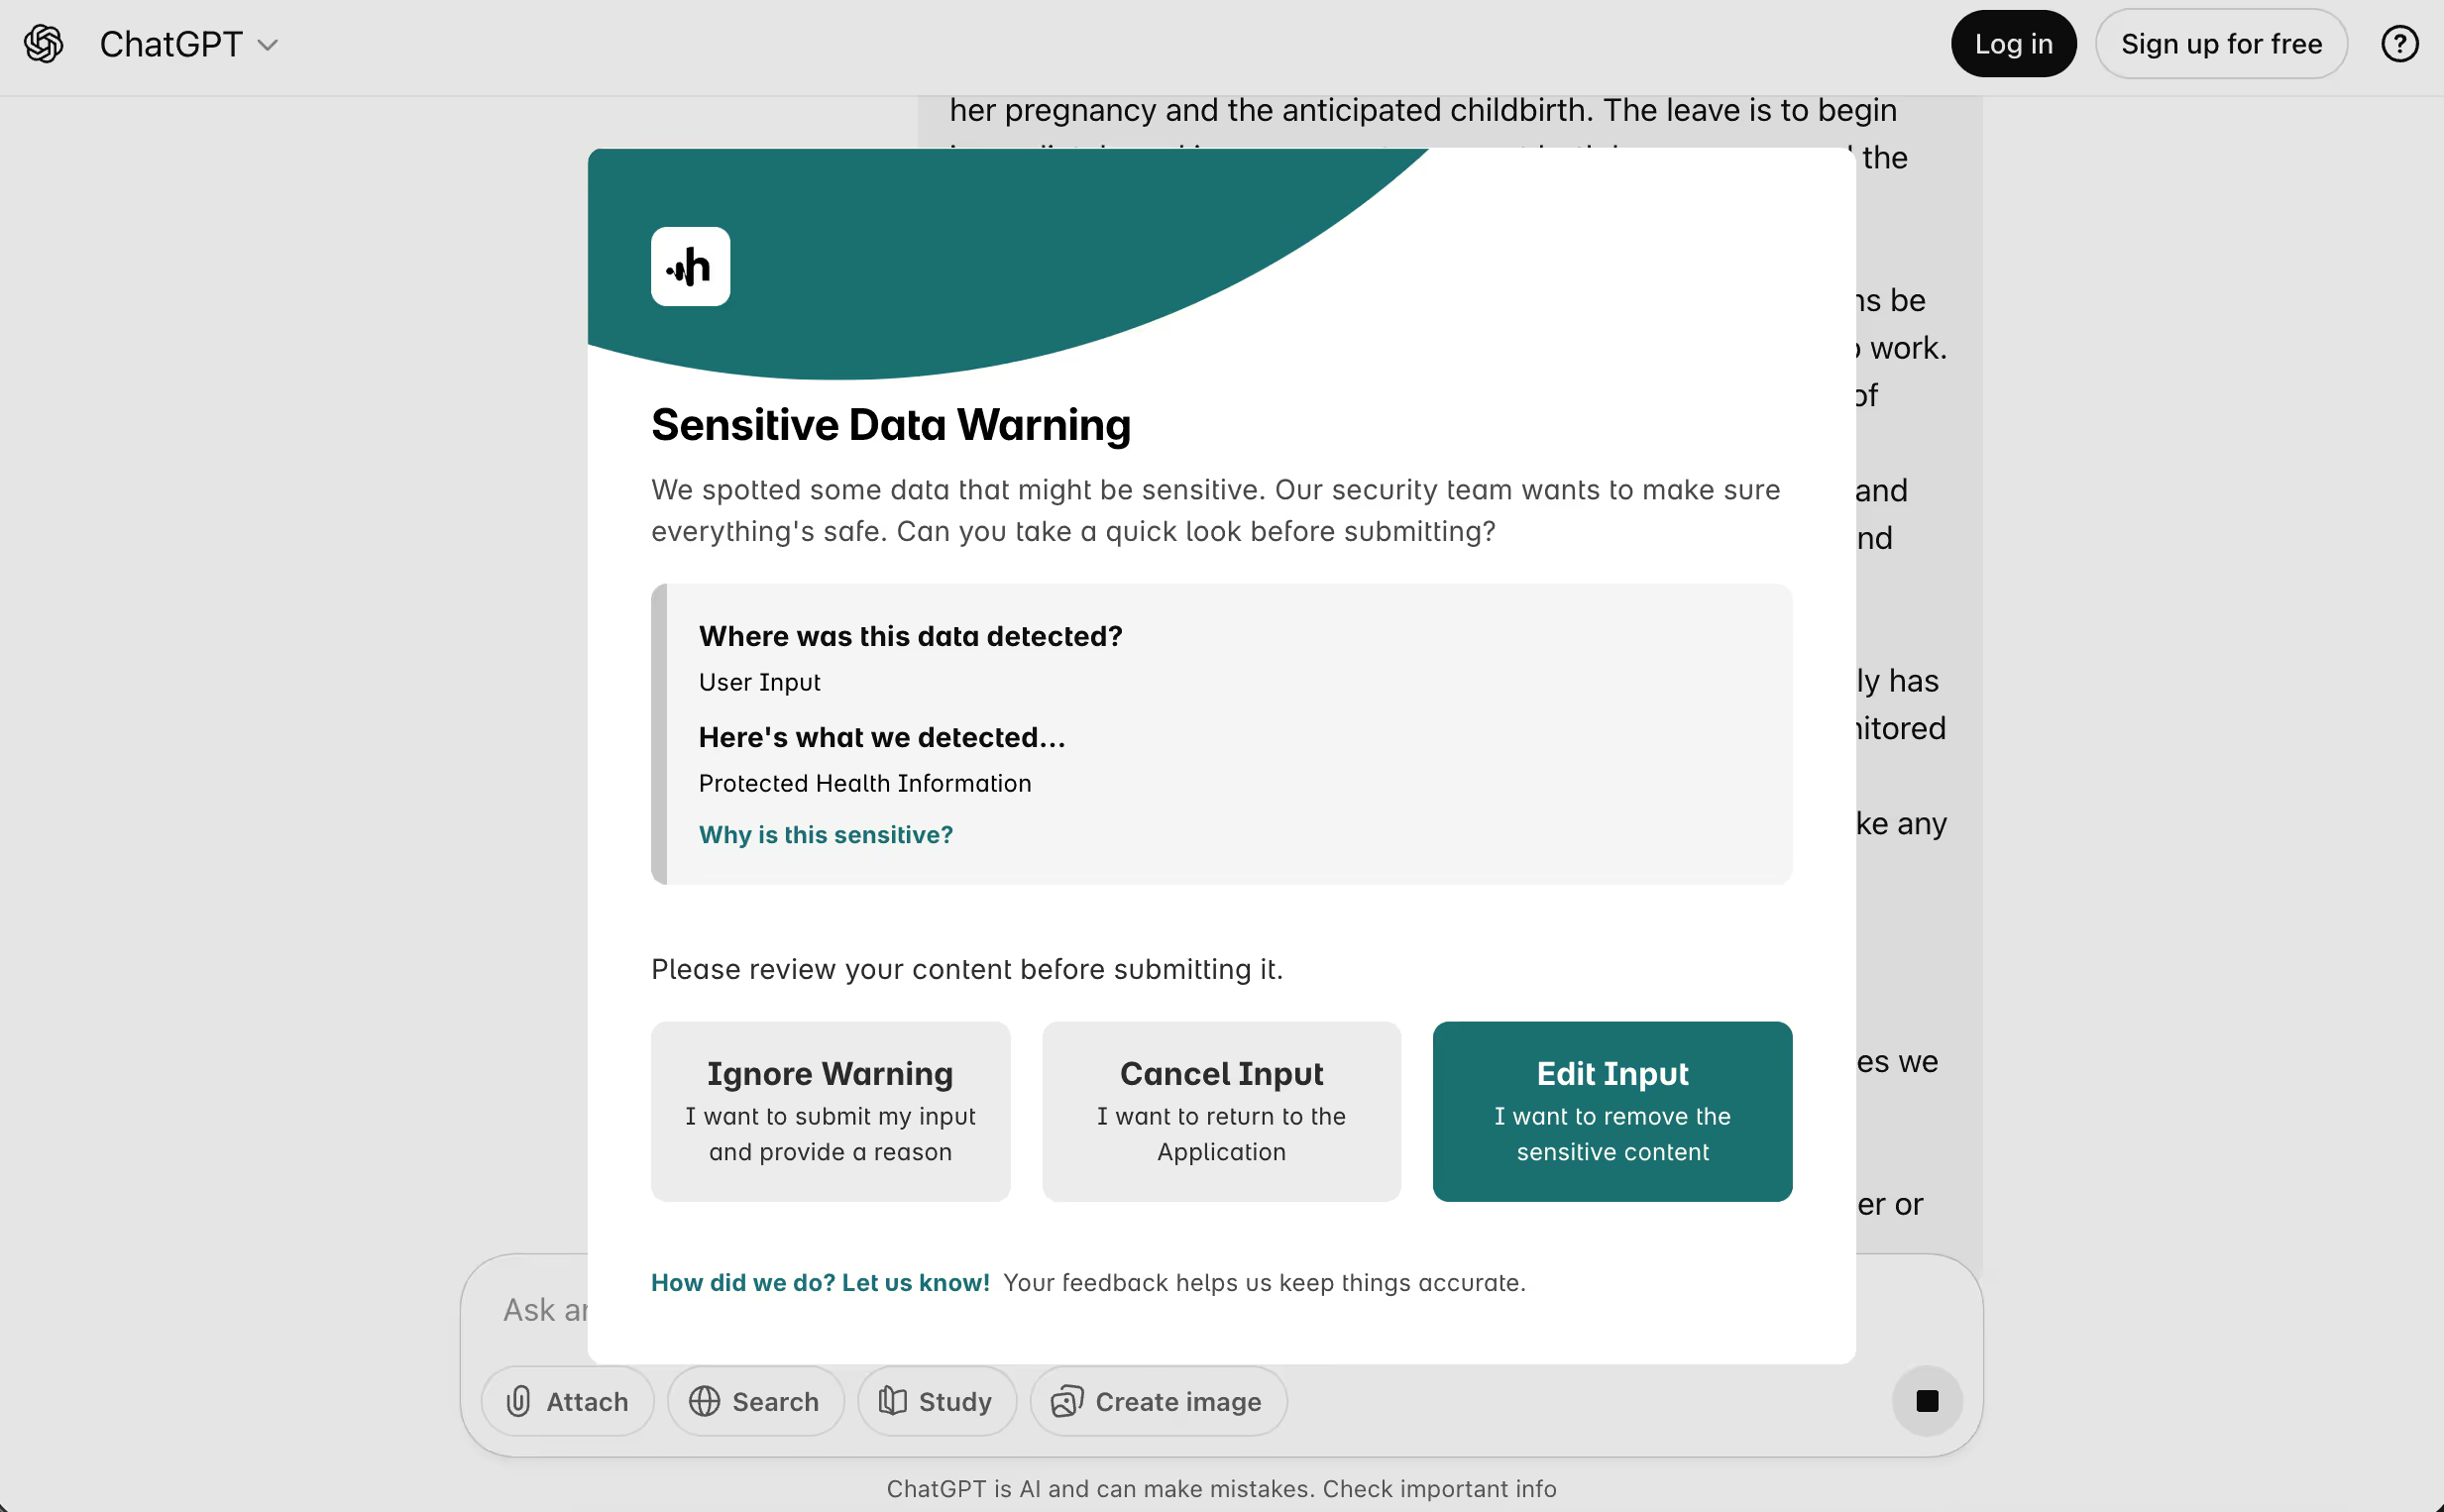
Prevent the upload of protected health information and personally identifiable information to non-compliant models.
Harmonic works in the browser and on the endpoint to detect sensitive data and block it from unapproved AI tools, so patient and client data stays out of public model training.
03Contracts
Enforce contractual customer data protections
Your customers trust you with their data. Harmonic detects customer information and prevents it from leaking into public AI tools.
That helps you enforce data residency and training policies, and stay compliant with the commitments in your own client contracts.

Top resources
Resources for regulated teams
Policy templates, platform evidence and the controls auditors ask about.
Frequently asked questions
Quick answers about GenAI compliance
Short, direct answers to what security, risk and compliance teams ask before bringing Harmonic in.
Can traditional DLP detect sensitive data in AI prompts?
Traditional regex-based DLP struggles with conversational AI, because prompts are unstructured, contextual, and often contain legitimate business information that patterns cannot distinguish from sensitive data. That leads to false positives and monitor-only deployments.
Do Netskope and Zscaler offer AI-specific controls?
Some SASE vendors offer limited AI controls for a small number of high-profile domains like ChatGPT or Copilot. Those controls require per-domain integrations and do not cover the full spectrum of AI tools, embedded AI features, or agentic workflows.
What is Harmonic Security's technical differentiator?
Harmonic uses purpose-built small language models that understand user intent and sensitive data in milliseconds. This low-latency analyzis lets you understand AI usage and enforce inline controls without slowing work down.
How is Harmonic Security deployed?
Harmonic can be installed with a range of MDM tools, such as Kandji, Intune or Jamf.
Get started
Build your AI guardrails for a regulated business
Gain the visibility and control you need to guide AI use with confidence. Most teams see first insight in about 30 minutes.
What you'll see with Harmonic Security
- Your full AI usage footprint: every surface, every team, every exposure.
- Inline guardrails that coach, warn, or block, firing in under 200ms.
- See and control what AI agents are actually doing.
- Coverage of browser, endpoint and MCP.
- Deployment in minutes via Intune, JAMF, or Kandji.
