Solutions / AI Governance
Turn your AI policy into controls you can prove
See how your workforce uses AI, guide people toward safe use while they work, and have the reporting ready when an auditor, regulator or board asks how AI is governed.
Talk to us about securing AIWho we work with
Why Harmonic for governance
From written policy to working controls
An AI policy only counts if it gets applied. Harmonic applies yours to the AI your employees actually use, so you know where it holds, where it doesn't, and what to change next.
01Visibility
Know what AI is in use and what it's used for
Harmonic builds an inventory of the AI apps your workforce uses, who uses them and for what work. That becomes your AI register, kept current from real activity rather than surveys.
Usage Intelligence groups the activity into use cases, so you can see where AI creates value and where it creates risk.

02Guidance
Guide people, and tell them why
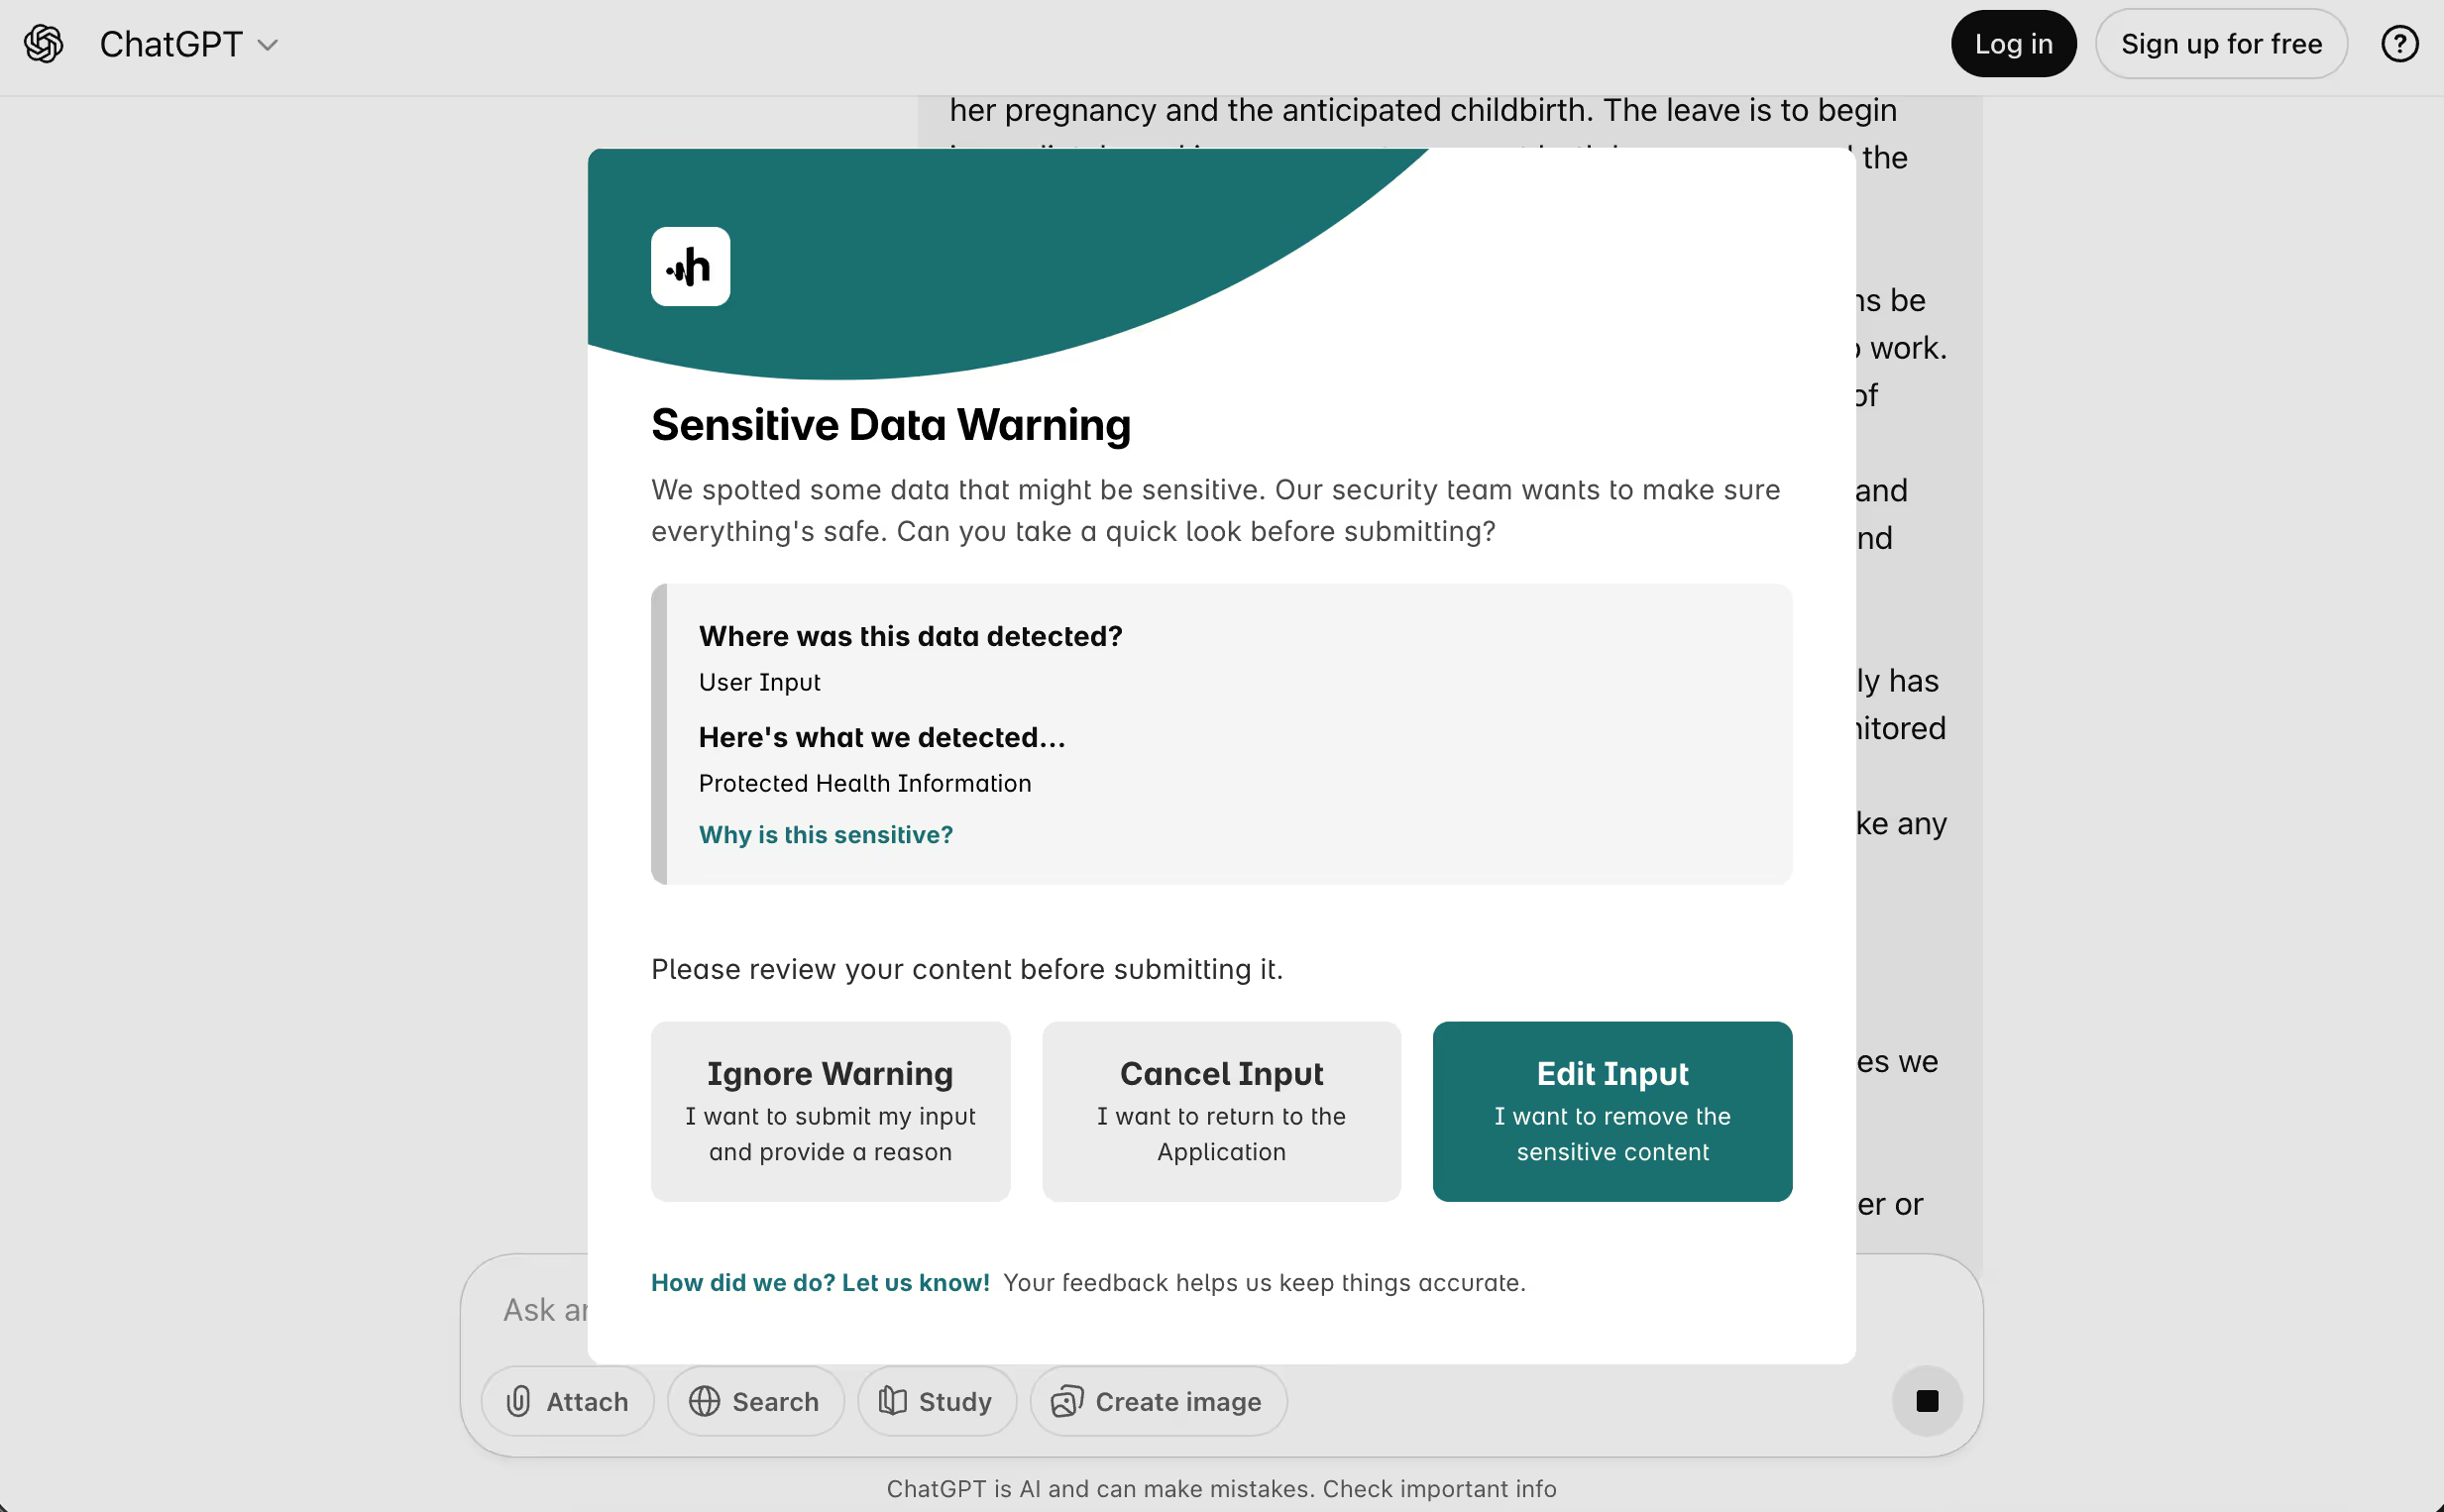
Blocking pushes people toward personal accounts and tools you can't see. Harmonic reads the intent and context of each interaction and only steps in when the data calls for it.
Your team decides what happens next: a warning the user can override with a reason, or a block. Either way, Harmonic explains exactly what it found and why it matters, so people learn what's safe to share.
03Proof
Reporting ready for audits and regulators
Auditors want evidence, not a policy document. Harmonic records which tools are approved, how policy was applied, what was coached or blocked, and where sensitive data was exposed.
Configurable retention, role-based access, employee masking and EU or US hosting keep the data behind those reports under your control.

Top resources
Resources for building AI governance
How other teams govern AI, and what the latest usage data says.
Customer story
Apax
How Apax moved from AI blind spots to usage intelligence and in-line coaching.
Customer story
Demonstrably compliant
How a global law firm proved its AI policy was being followed.
Report
2026 AI Usage Index
Where work really happens across free, paid and enterprise AI accounts.
Datasheet
Harmonic Command
Governance and control for employees and the agents they use.
Frequently asked questions
Quick answers about AI governance
Short, direct answers to what security and IT teams ask before bringing Harmonic in.
Why can't security teams just block all AI tools?
AI is embedded in approved productivity tools like Google Translate, Microsoft Copilot and Salesforce, so blocking AI would block core business functions. Employees will also use personal devices and accounts when corporate access is restricted, creating greater shadow AI risk.
How does Harmonic help with AI audits and compliance?
Harmonic keeps a record of which AI tools are in use, how your policies were applied, and where sensitive data was coached or blocked. Security and compliance teams use that evidence to answer auditors, regulators and boards, and to keep an AI register current without manual surveys.
Who can see what employees do with AI?
You decide. Role-based access controls who can view prompt data, retention periods are configurable, and employees can be masked or excluded. Harmonic is built for coaching and governed access, and it does not train on customer data.
Do Netskope and Zscaler offer AI-specific controls?
Some SASE vendors offer limited AI controls for a small number of high-profile domains like ChatGPT or Copilot. Those controls require per-domain integrations and do not cover the full spectrum of AI tools, embedded AI features, or agentic workflows.
What is Harmonic Security's technical differentiator?
Harmonic uses purpose-built small language models that understand user intent and sensitive data in milliseconds. This low-latency analysis lets you understand AI usage and enforce inline controls without slowing work down.
Get started
Build your AI guardrails for the whole workforce
See how your workforce uses AI today and what it would take to govern it, with reporting you can put in front of an auditor.
What you'll see with Harmonic Security
- Your AI register built from real use: which tools, which teams, what data.
- Warnings or blocks, your choice, each with a clear explanation so people learn what's safe to share.
- Audit and compliance reporting that shows how your AI policy was applied.
- Usage Intelligence showing where AI creates value by team and use case.
- Privacy controls including role-based access, employee masking and configurable retention.
