
AI Detection and Response for Workforce AI
Discover the AI tools and workflows employees use, detect sensitive-data exposure and risky actions in context, and respond while the work is happening.
Harmonic Security AIDR
AI risk is created in the interaction: a prompt, file, response, connector call, or agent action. Harmonic applies detection and response to that layer, giving security teams the visibility and control to enable workforce AI with confidence.
The result is fewer blind spots and faster intervention based on lower-noise detection.
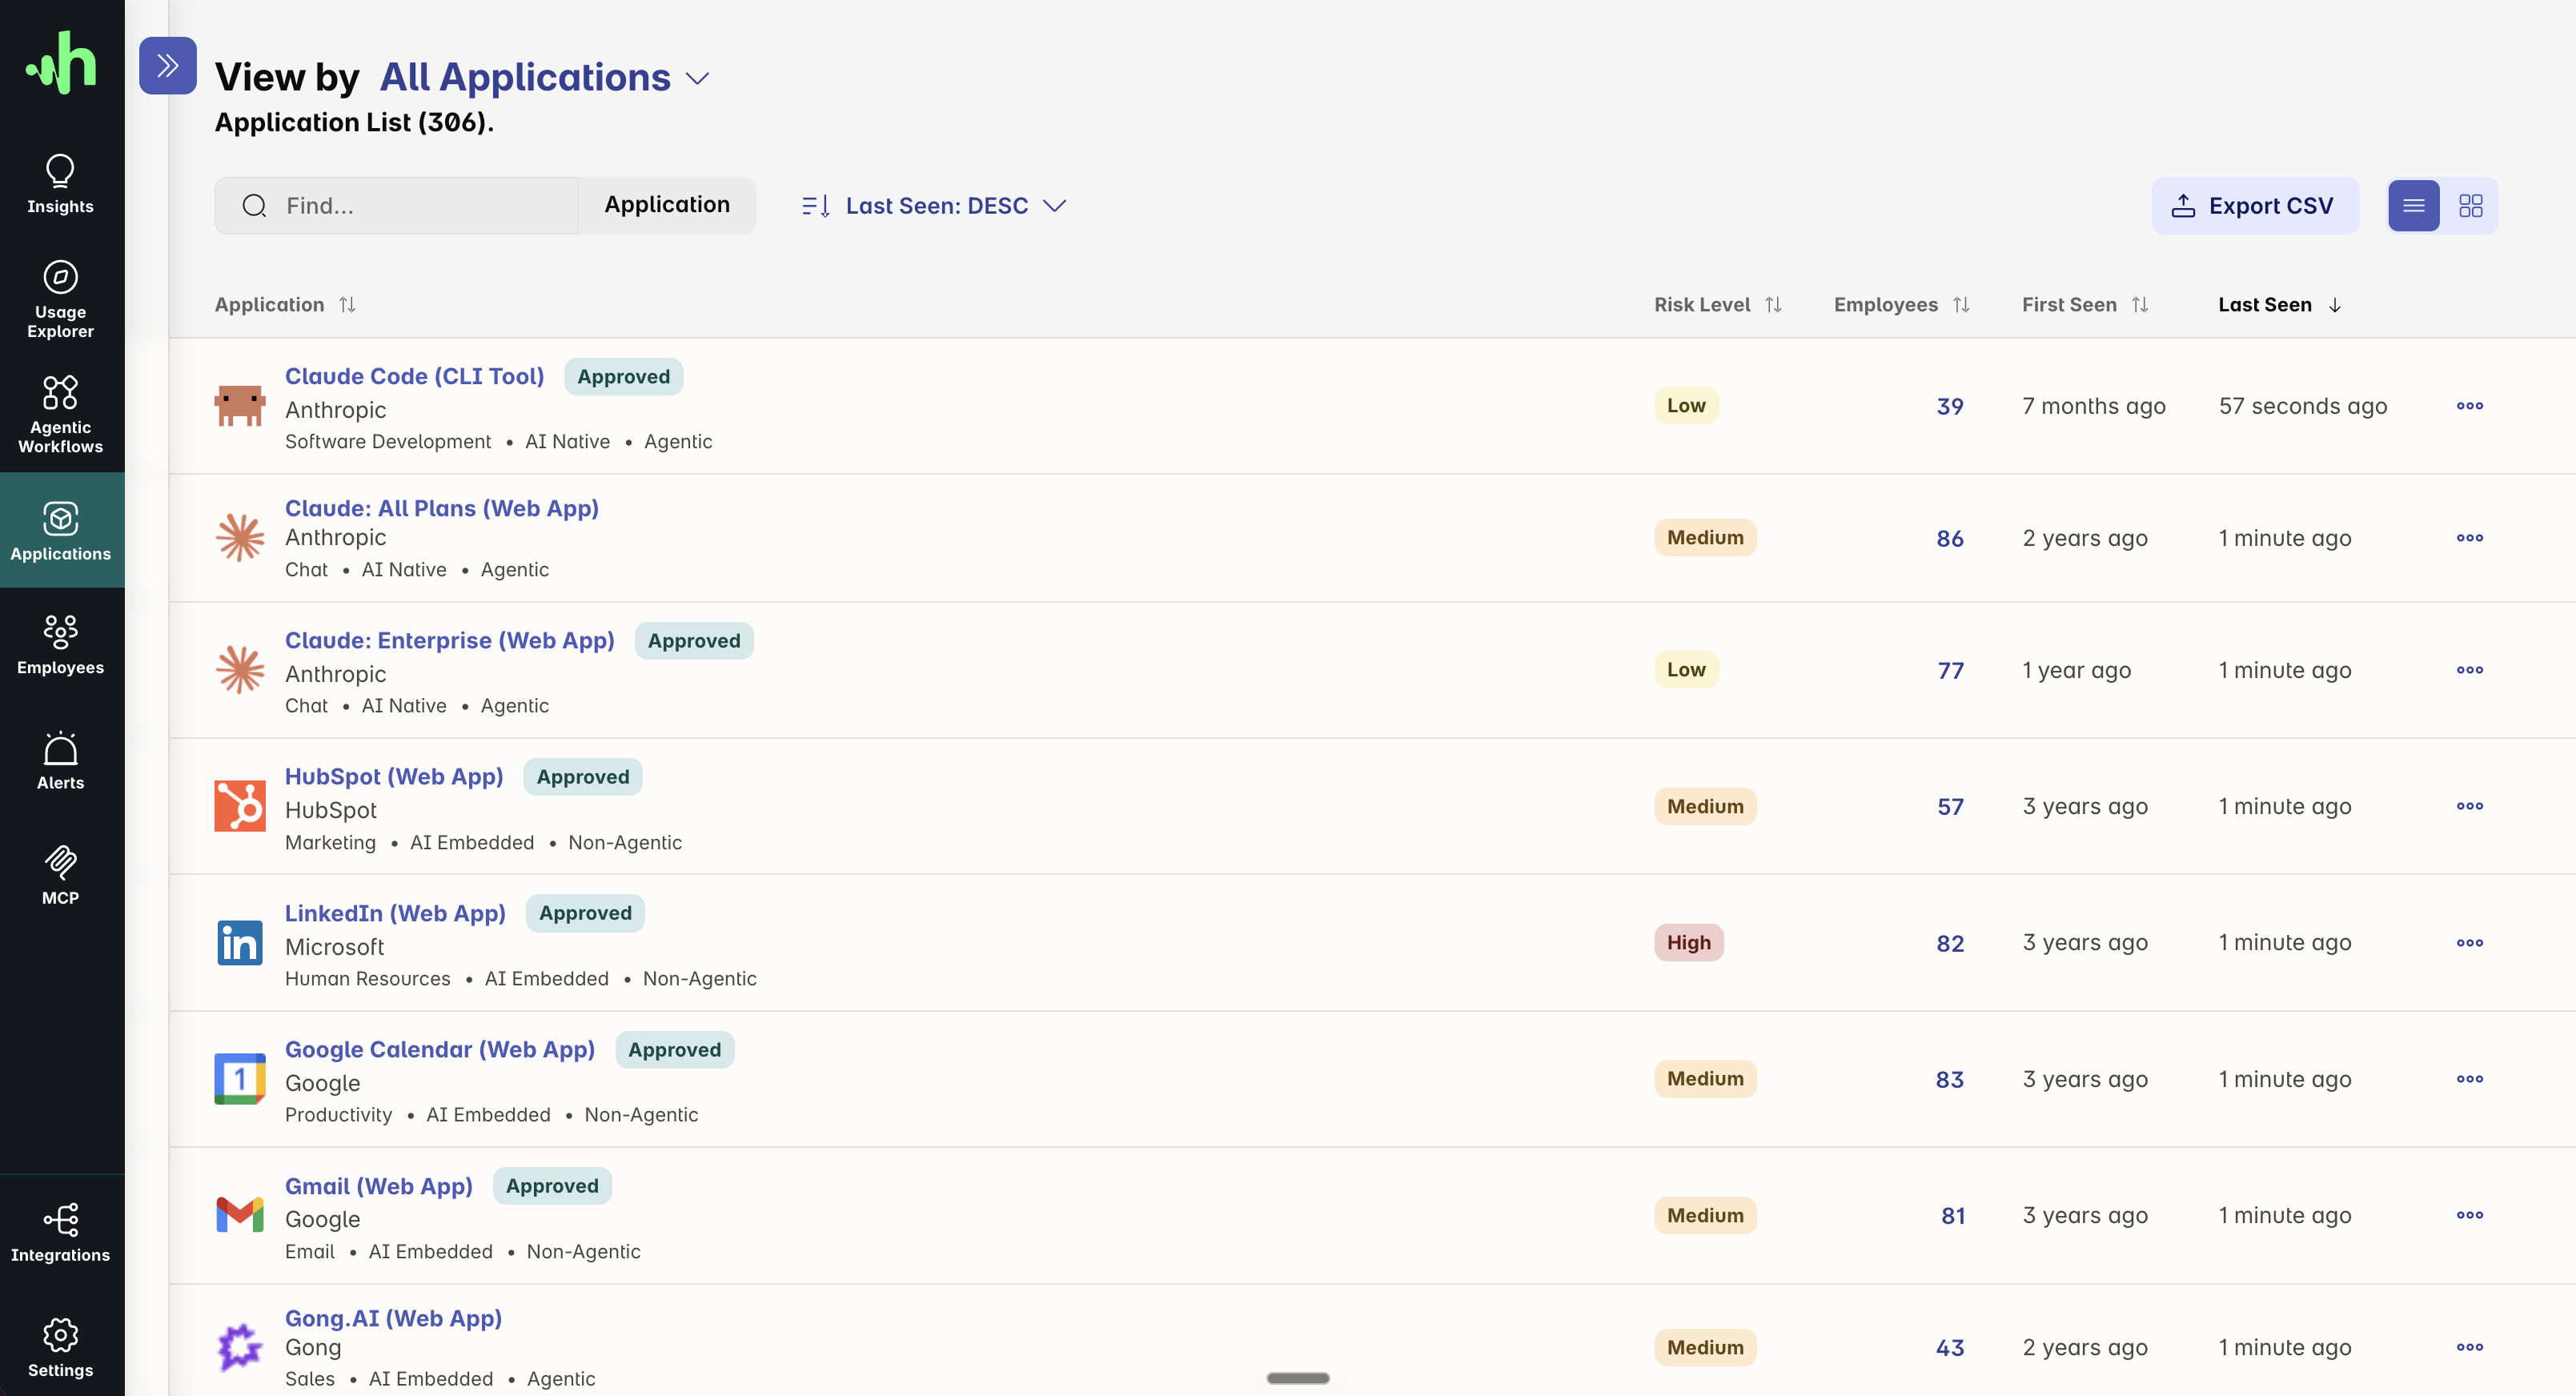
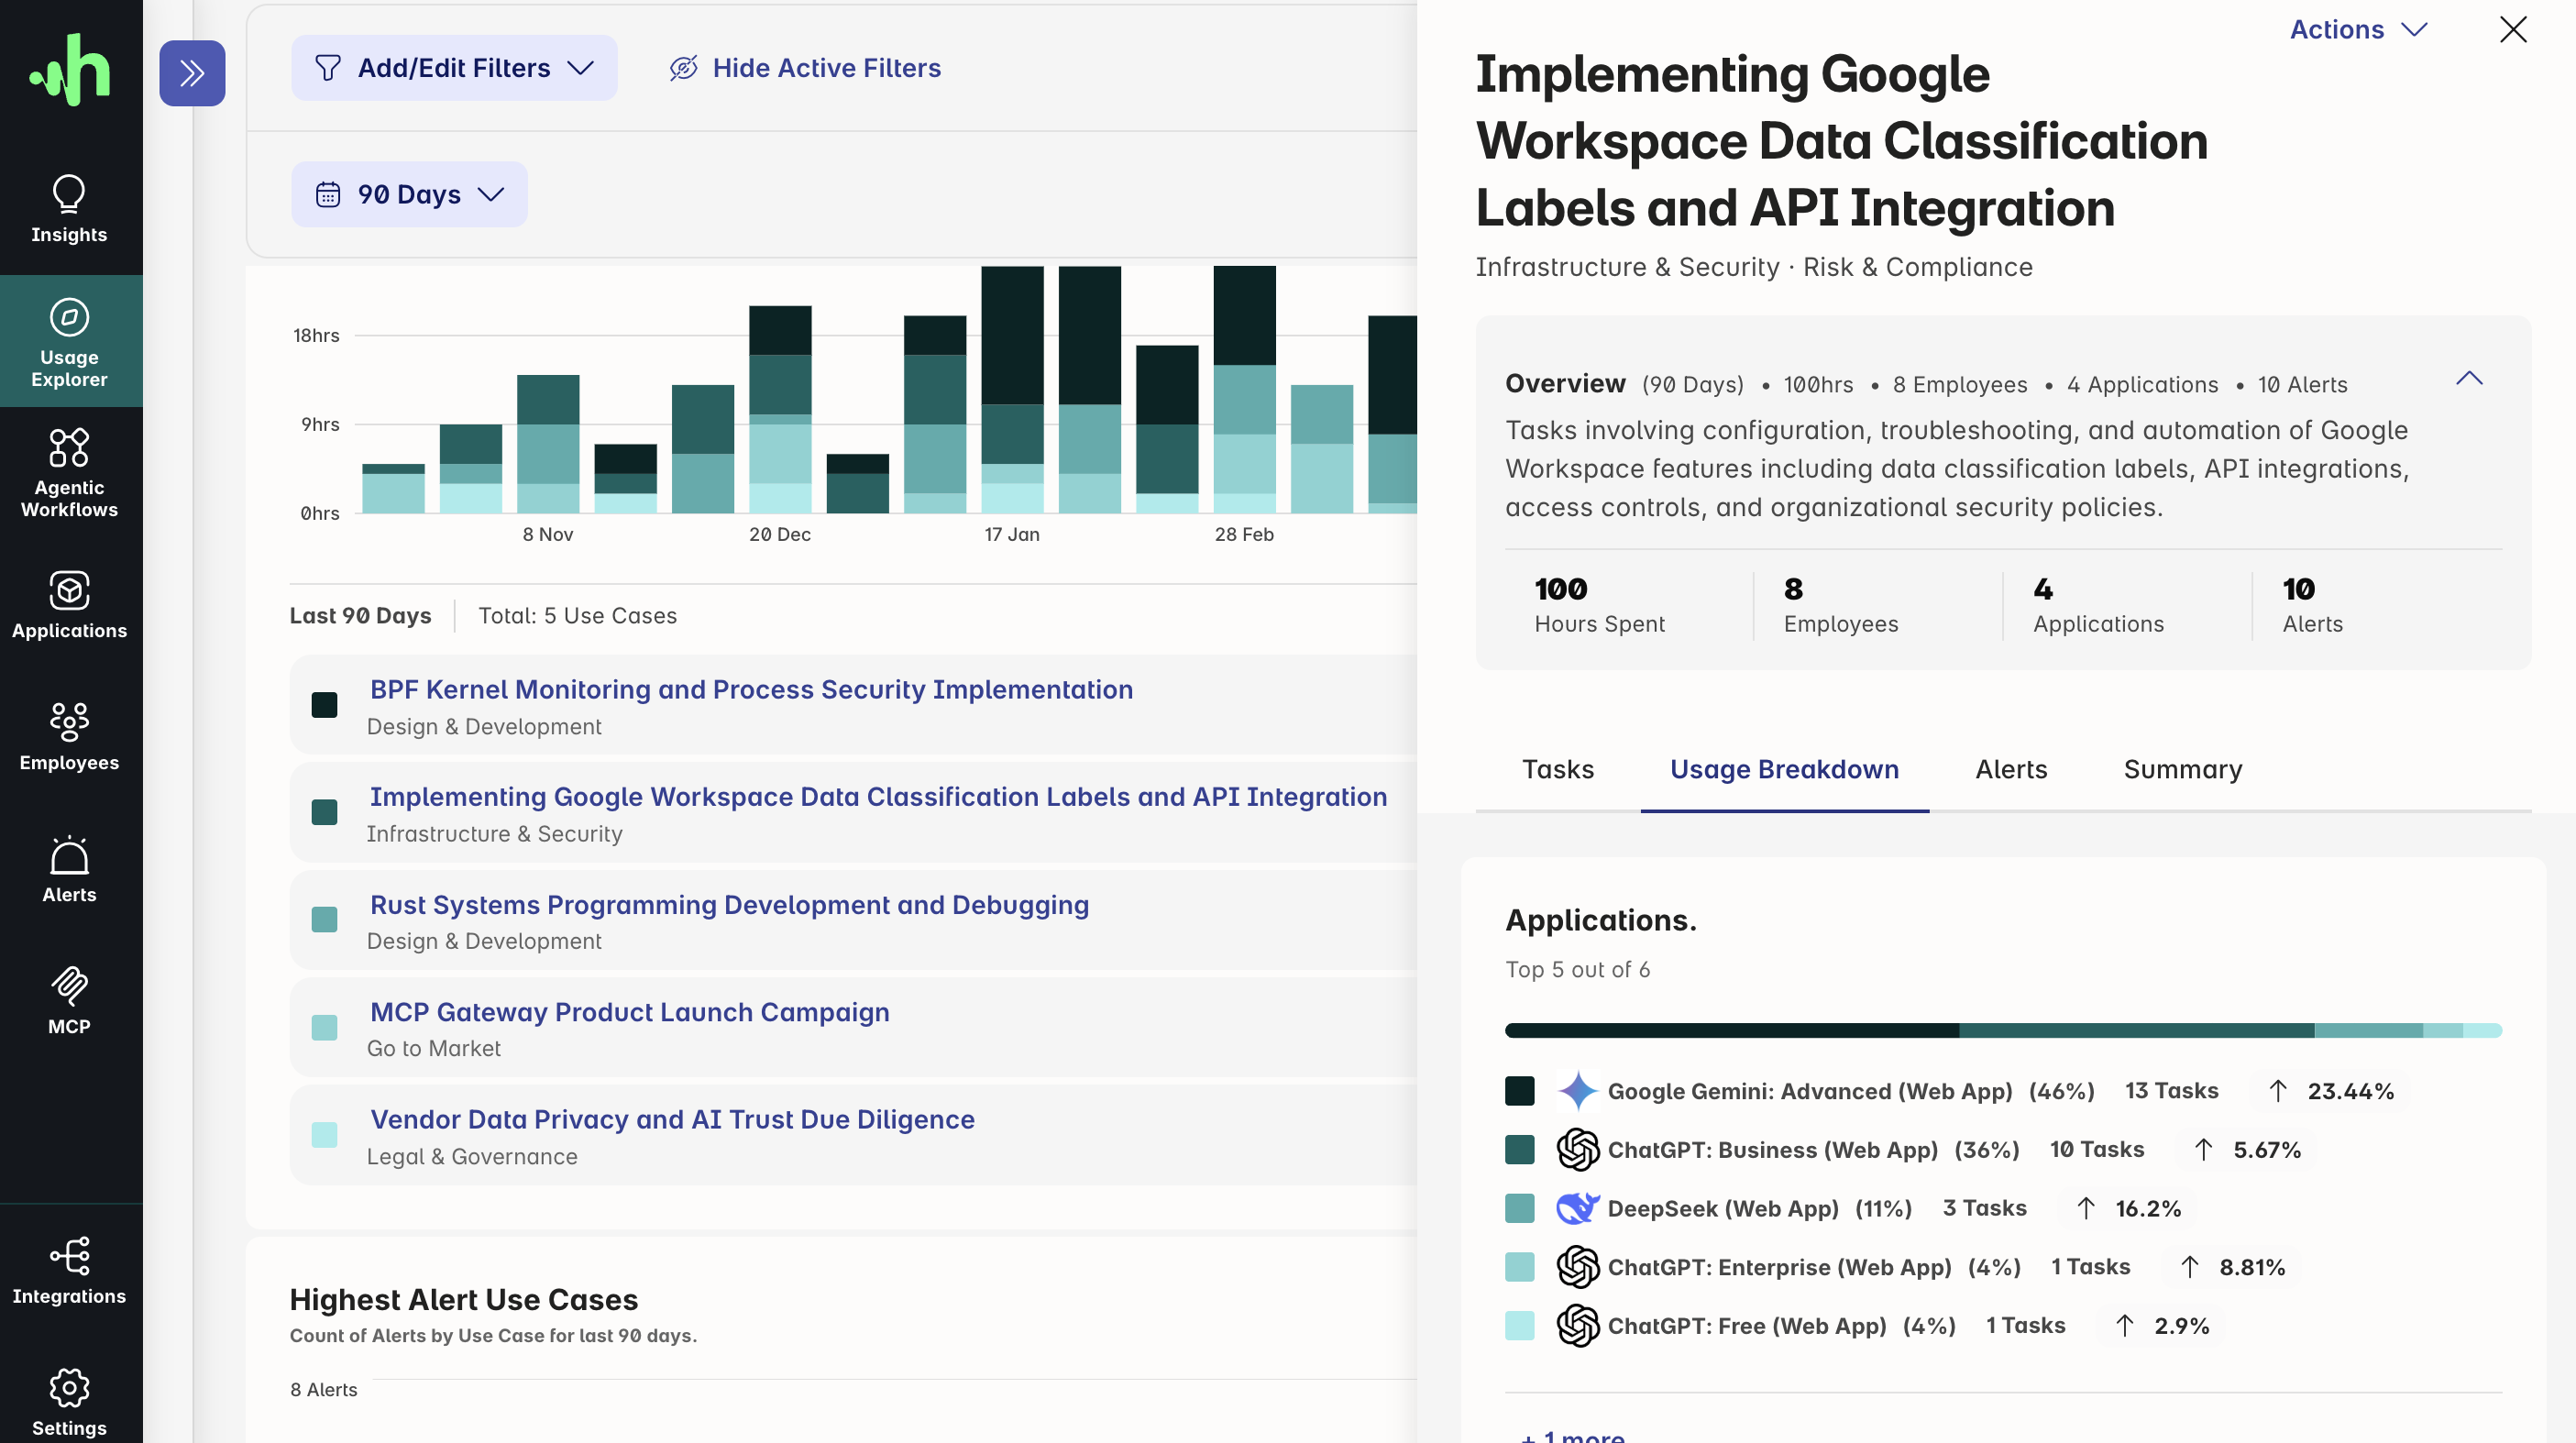
See how AI is used across the workforce
Build a living inventory of the AI applications and workflows employees actually use. Understand which teams are adopting AI, what work it supports, where unsanctioned tools appear, and which use cases are producing the most risk.
Give security and AI leaders the evidence they need to guide policy, investment, and enablement.
Understand risk in context
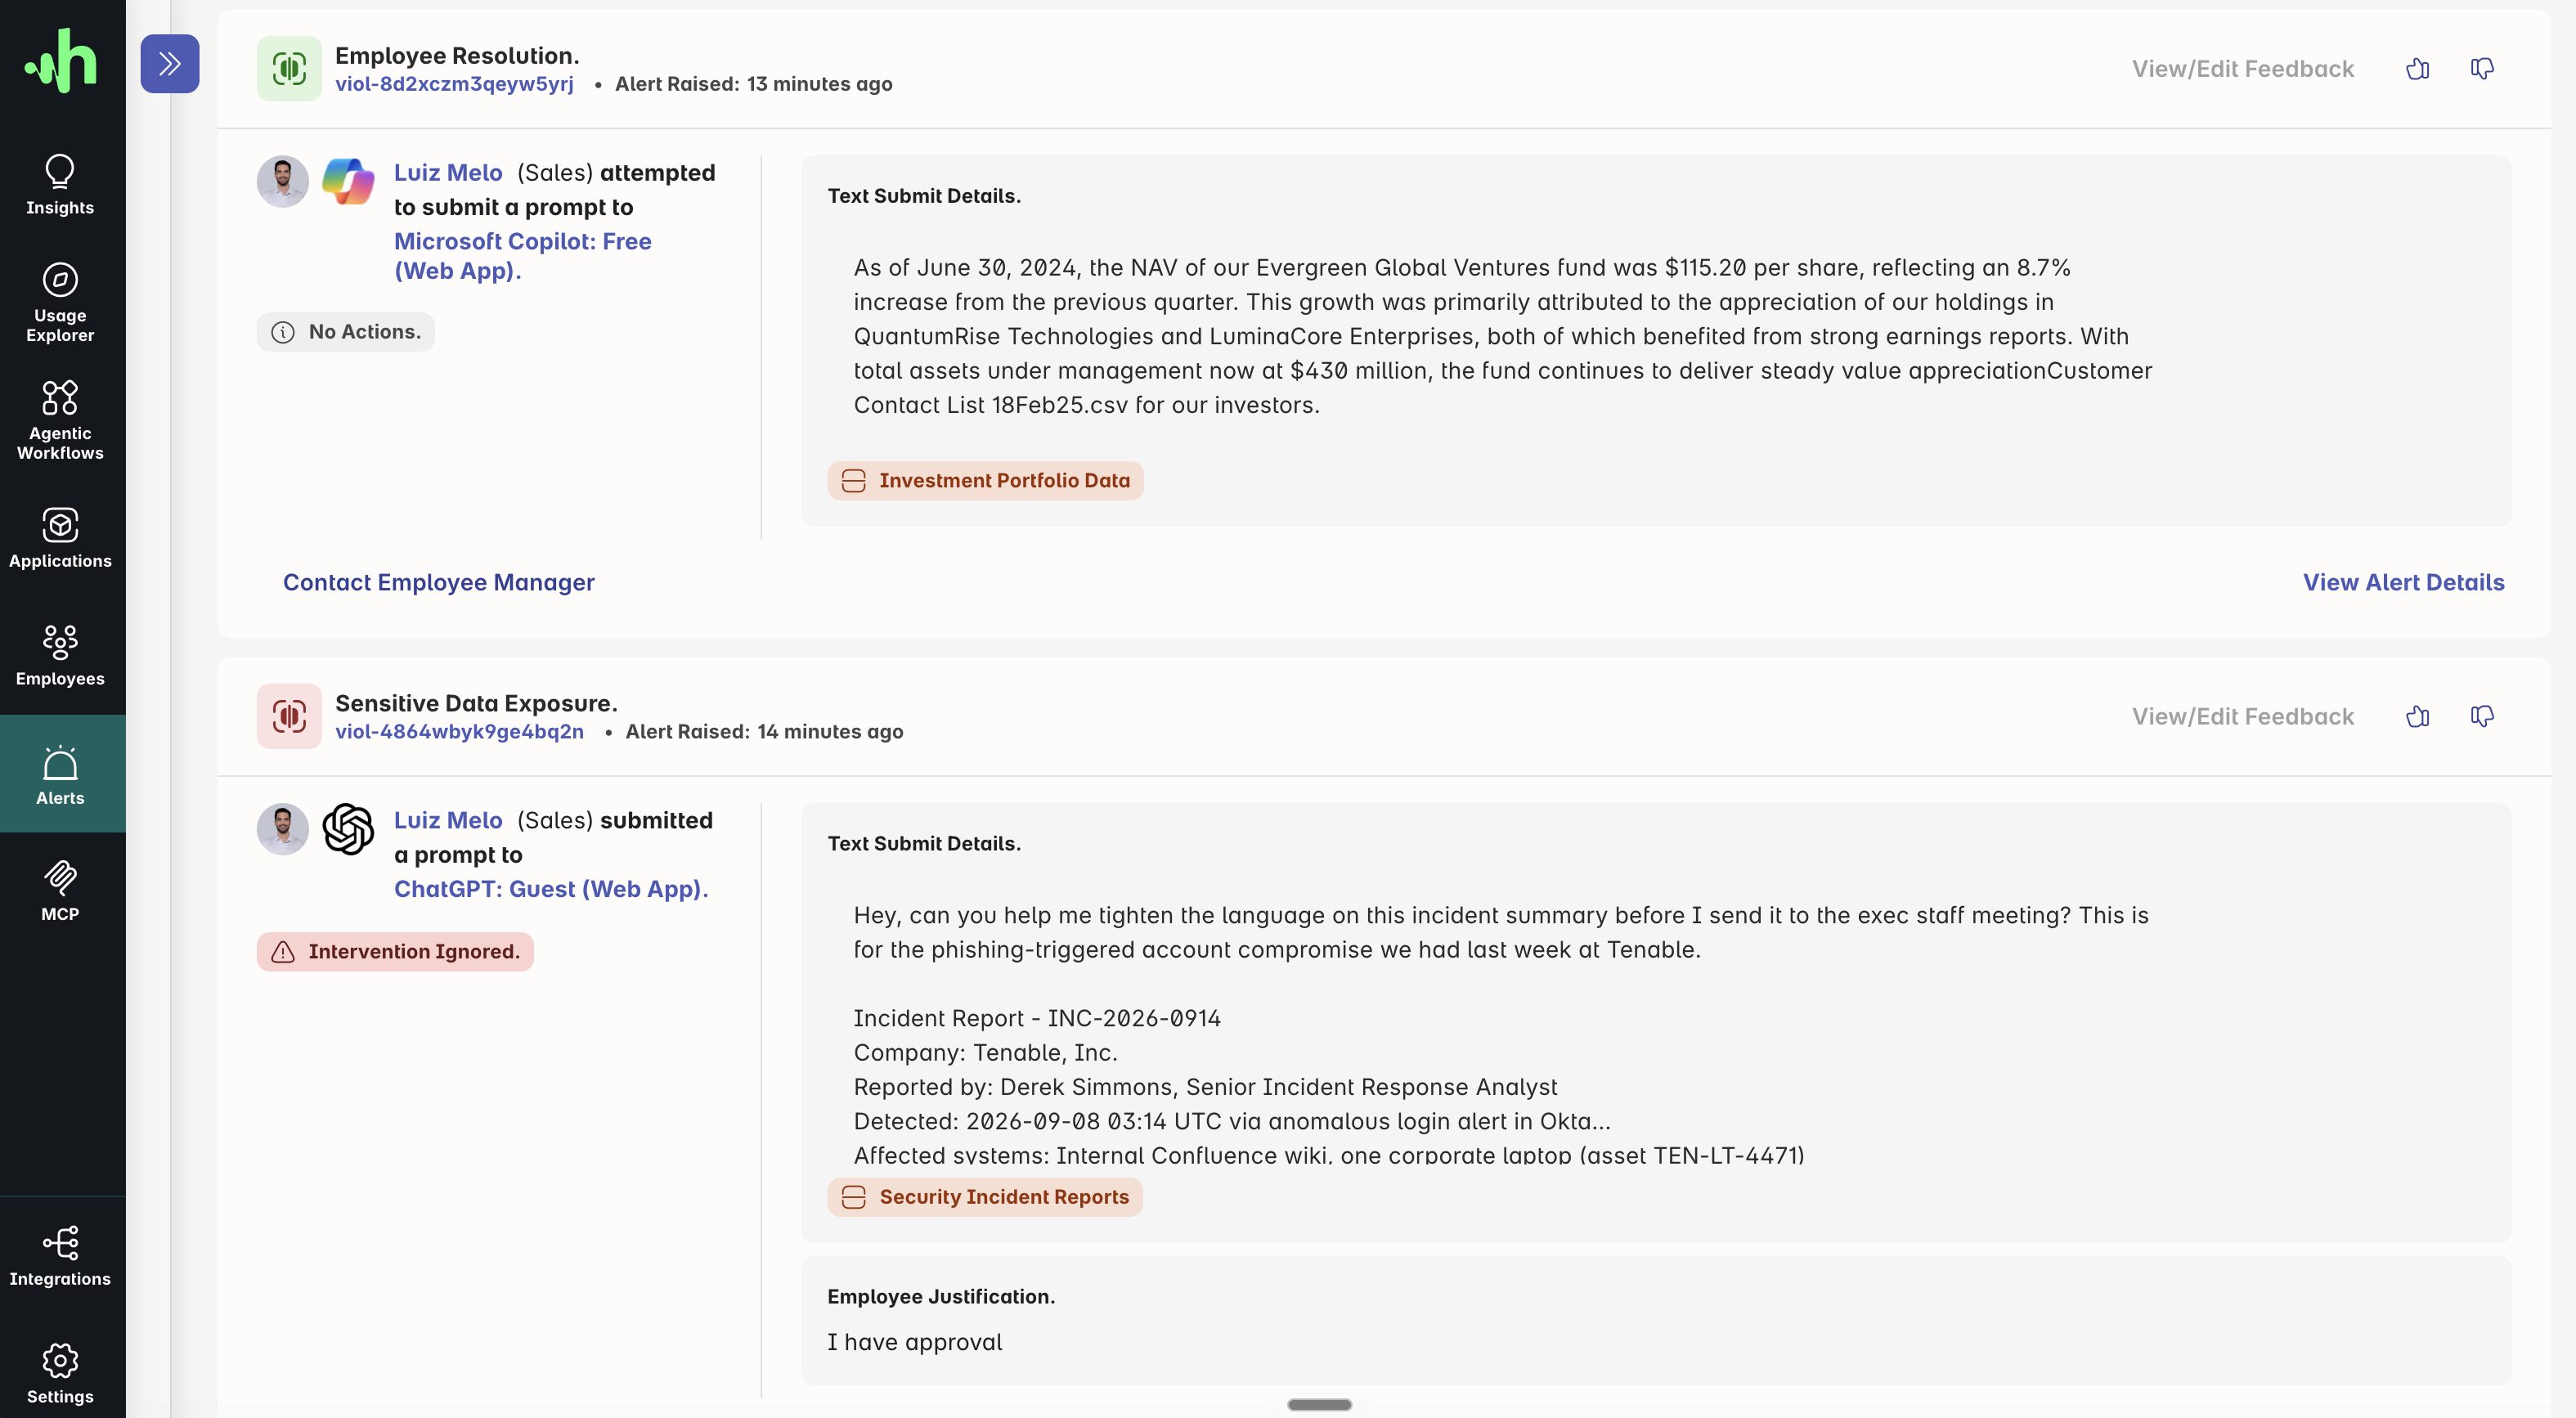
Harmonic Security's purpose-built models analyze the intent and context of prompts, files, responses, connector calls, and agent actions. They can distinguish routine work from genuine exposure.
This context gives security teams more precise detections and fewer false positives, so they can focus on the events that matter.
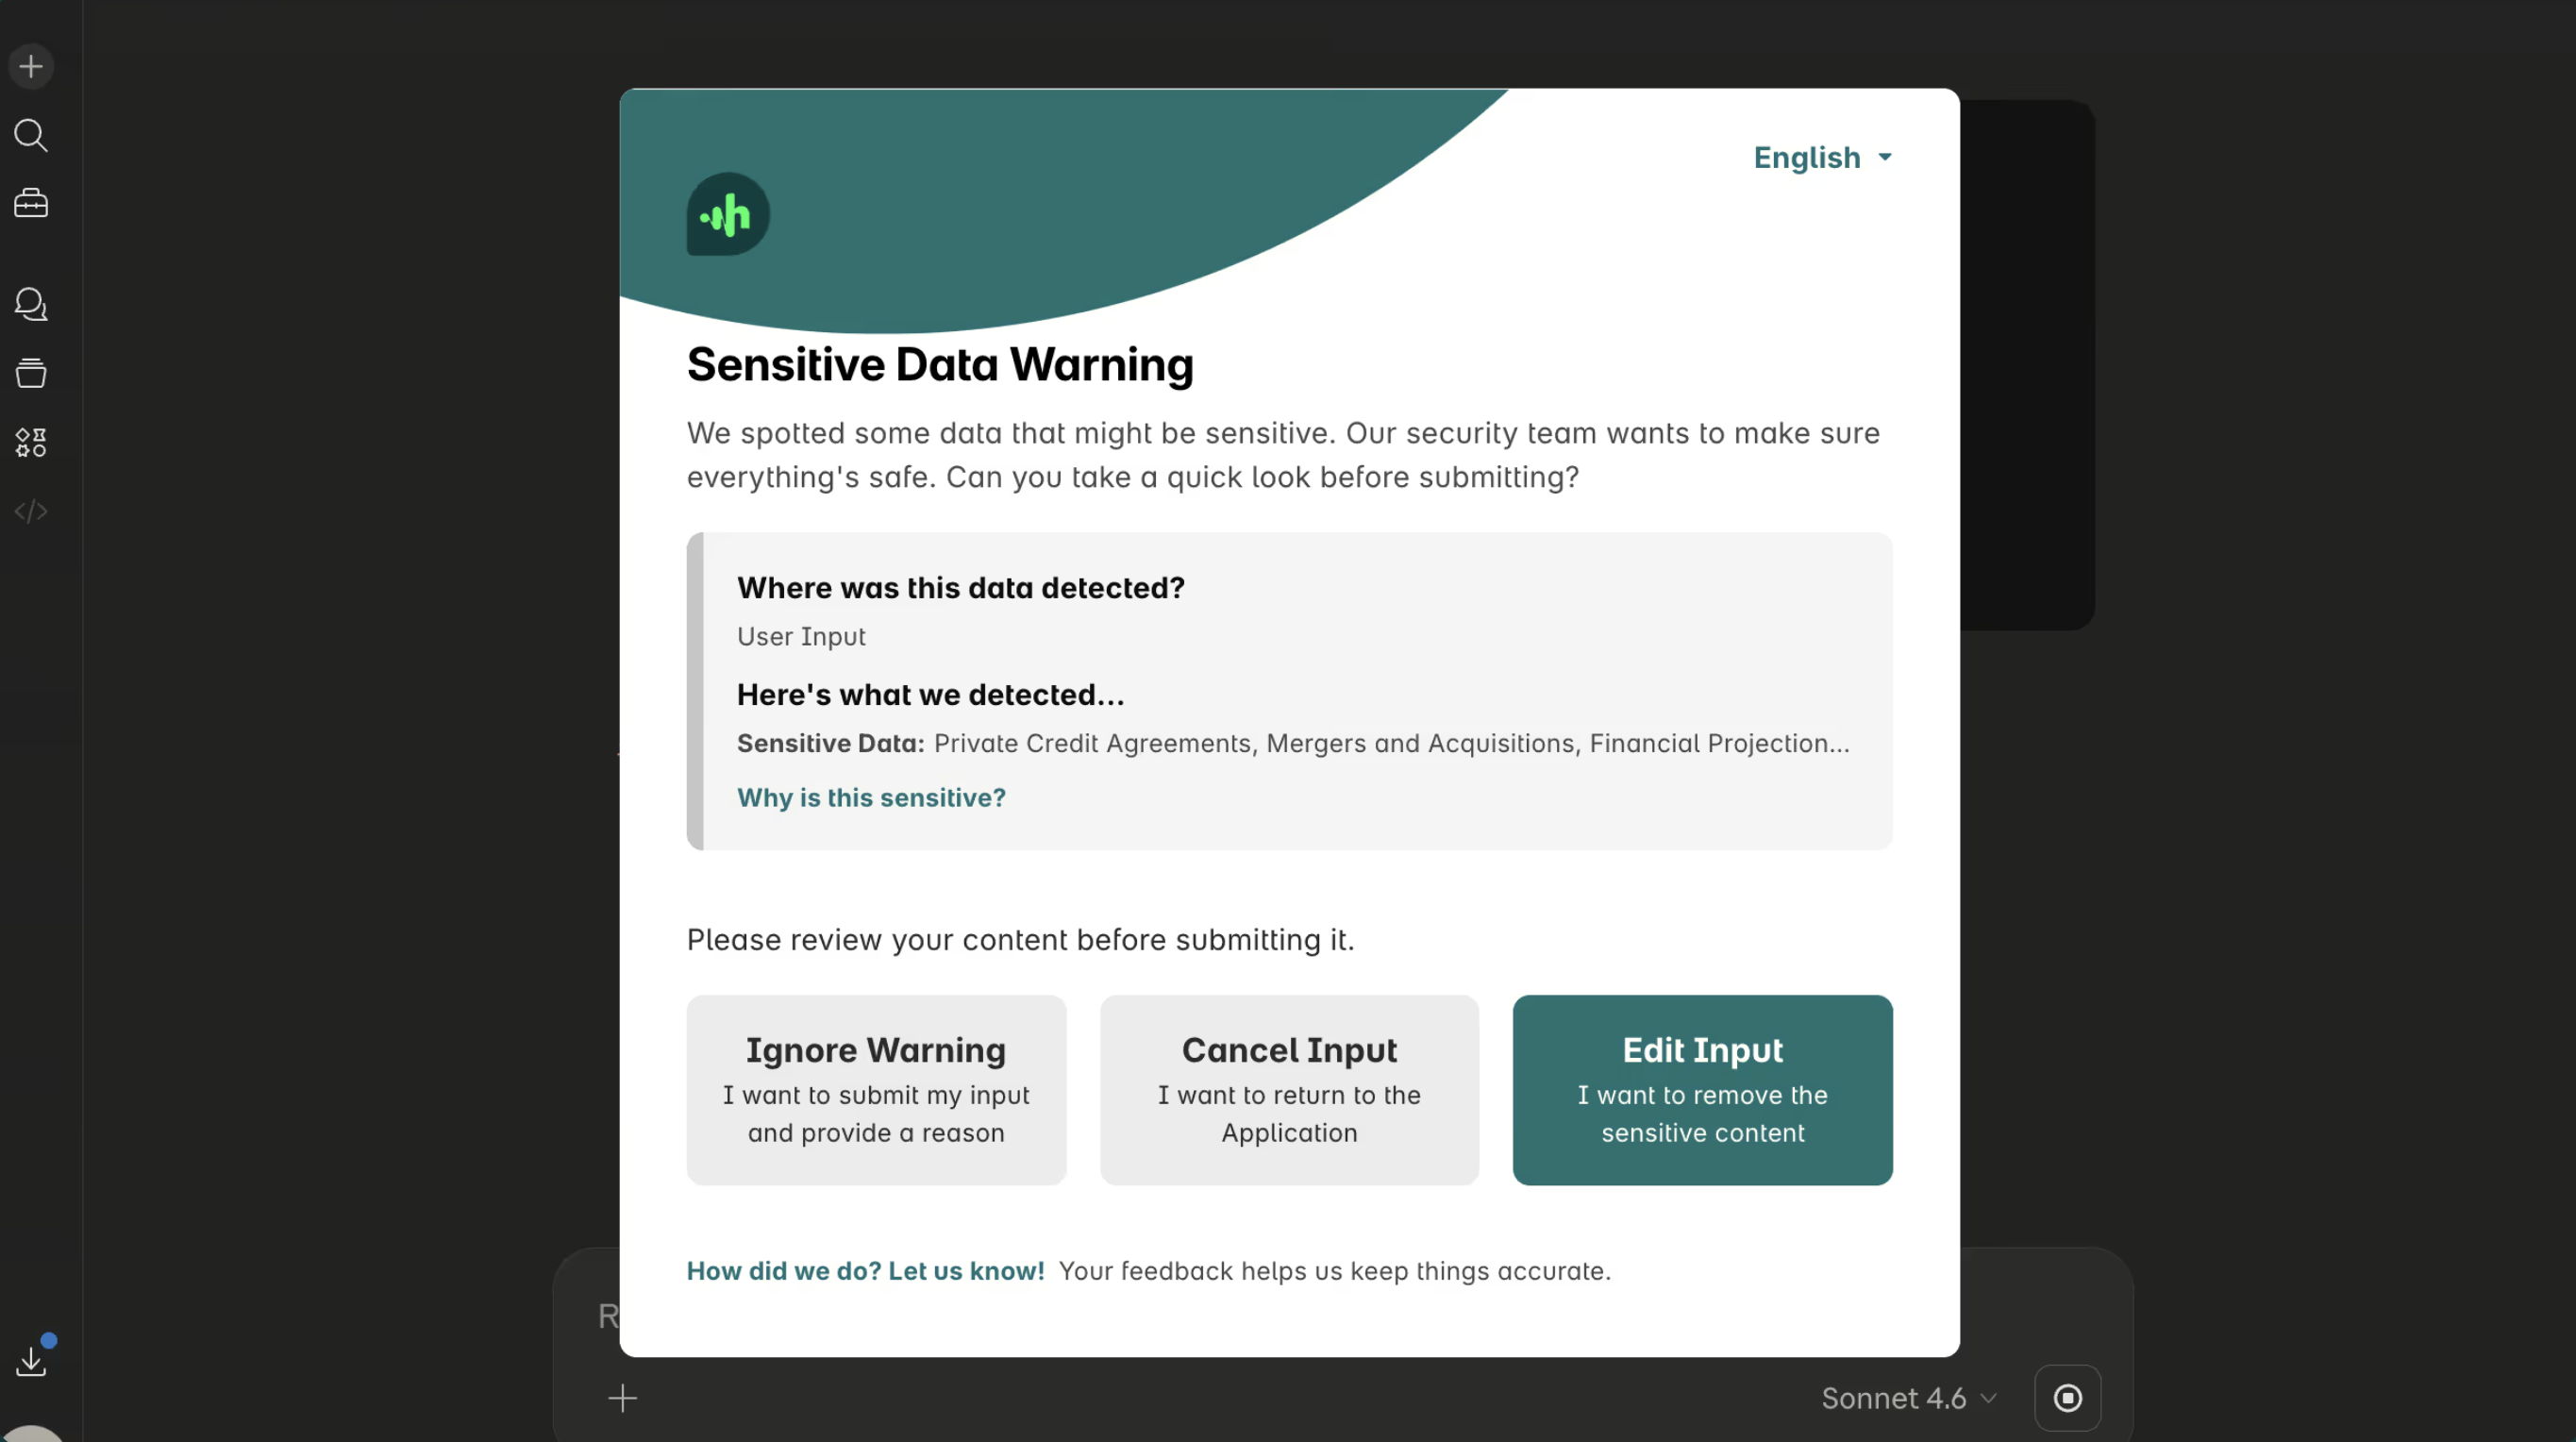
Implement guardrails without interrupting work
Choose the response that fits the situation. Harmonic can record an event, coach the employee, request a justification, warn them, or block a supported interaction or agent action.
Inline interventions explain what triggered them and how to continue safely. Teams can stop high-risk behavior before it becomes an incident while legitimate work continues.
Top Resources for Security Teams


FAQs
Quick answers about Harmonic Security
EDR is designed to monitor processes running on the endpoint and detect malware. Crowdstrike and other vendors have minimal visibility into what's being done by employees within AI tools on the desktop. They'll know that an application is being run, and they could block it entirely, but they are unable to provide the task level intelligence and granular guardrails needed to safely use AI.
You can, and it's a reasonable starting point. The difficulty is that when you block tools without a suitable alternative, employees will inevitably find ways to use them anyways, often via personal accounts that are even more risky.
And even for officially sanctioned tools, you need a solution to provide granular guardrails over the actions taken within them. For example, an oficially approved coding agent could still delete a repository or push sensitive customer data into production.
Harmonic uses purpose built small language models that understand user intent and sensitive data in milliseconds. This low latency analysis lets you understand AI usage and enforce inline controls without slowing work down.
Mike Janielis
Principal Information Security Architect
Huy Ly
Director IT Infrastructure/Security,
Monolithic Power Systems
Build Your AI Guardrails Now
Gain the visibility and control you need to guide AI use with confidence.